
More than two-thirds (69%) of data breach victims in the past year were affected by a third-party breach, a new report by financial and risk advisory provider Kroll has found.
Of those individuals, most (79%) had their data accessed following the compromise of a technology company during the period June 2025 to June 2026.
This is far higher than the proportion of third-party data breaches emanating from other industries, which includes finance (9%), insurance (6%) or healthcare (5%).
Incidents affecting technology firms also caused 60% of the total number of data breach victims – whether emanating from a single organization or as part of a supply chain breach – over the 12-month period. This was followed by insurance (10%), finance (8%), healthcare (8%) and education (7.5%).
Among all security leaders surveyed for the Kroll report, published on October 22, 69% said their organization had suffered a breach in the previous 12 months, while 34% reported experiencing more than one.
Finance and Professional Services Most Breached Sectors
Despite the tech sector causing the vast majority of individual data breach victims, it was only the seventh most commonly breached sector.
In first place was finance, making up 20% of breaches observed by Kroll. This was followed by professional services (20%), healthcare (15%) and retail (8%).
In contrast, technology only made up 6% of data breach incidents.
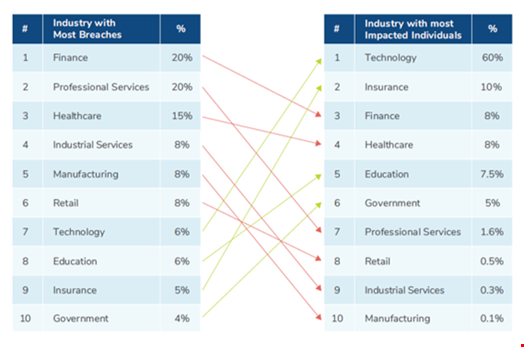
The researchers said the discrepancy shows that despite an industry seeming more susceptible to breach, such as finance or healthcare, the domino effect of a company breach in the technology sector could be much more extensive.
Denyl Green, global head of breach notification at Kroll, commented, "Across most of the major incidents we handled over the past year, a vendor, software supplier or service provider was the link between the initial breach and the organizations affected. One incident can reach businesses and individuals who have never dealt directly with the company where the compromise began."
Cybercriminal actors such as the Scattered Spider hacking collective are known to target IT service providers to gain access to their customers’ systems.
In October 2026, it was reported that a Chinese nation-state actor gained access to IT management software provider ConnectWise’s cloud infrastructure, enabling the group to target downstream customers.