Infosecurity News

KernelSU v0.5.7 Flaw Lets Android Apps Gain Root Access
A flaw in KernelSU 0.5.7 allows attackers to impersonate its manager app and gain root access to Android devices

Malvertising Campaign Deploys Modular PowerShell Malware PS1Bot
An ongoing malware campaign has been observed using malvertising to deliver PS1Bot, a PowerShell-based framework
FBI Shares Tips to Spot Fake Lawyer Schemes Targeting Crypto Scam Victims
The Bureau’s Internet Crime Complaint Center has provided a list of indicators for potential cryptocurrency scam victims to avoid a double whammy
Hacked Law Enforcement and Government Email Accounts Sold on Dark Web for $40
Abnormal AI said gaining access to such accounts provides opportunities for sophisticated fraud schemes that impersonate officials
Fortinet Warns Exploit Code Available for Critical Vulnerability
Fortinet reveals details of a new critical-rated vulnerability in FortiSIEM circulating in the wild
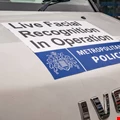
Campaigners Slam Expansion of Police Facial Recognition Schemes in UK
The UK government has announced 10 new live facial recognition police vans to be deployed around the country
Erlang/OTP SSH Vulnerability Sees Spike in Exploitation Attempts
A critical RCE vulnerability in Erlang’s OTP SSH daemon has been identified that allows unauthenticated command execution
Deepfake AI Trading Scams Target Global Investors
AI-powered trading platforms have been observed exploiting deepfake technology to trick investors with fake endorsements
Staffing Company Manpower Discloses Data Breach
The personal data of almost 145,000 people who were registered in Manpower’s systems was compromised
St. Paul’s Mayor Confirms Interlock Data Leak
Mayor of St. Paul, Minnesota, Melvin Carter, confirmed that employee data was published online by the Interlock ransomware gang
US Authorities Seize $1m from BlackSuit Ransomware Group
The US Department of Justice has announced the seizure of domains, servers and $1m in proceeds from the BlackSuit ransomware group
Microsoft Fixes Over 100 CVEs on August Patch Tuesday
Microsoft announced updates for 107 vulnerabilities on Patch Tuesday, including one zero-day
Hacker Alleges Russian Government Role in Kaseya Cyber-Attack
In a new investigation launched at DEFCON 33, Analyst1’s Jon DiMaggio revealed probable Russian government involvement in the Kaseya attack
GPT-5 Safeguards Bypassed Using Storytelling-Driven Jailbreak
A new technique has bypassed GPT-5’s safety systems via narrative-driven steering to elicit harmful output
29,000 Servers Remain Unpatched Against Microsoft Exchange Flaw
Over 29,000 Microsoft Exchange servers remain unpatched against a vulnerability that could allow attackers to seize control of entire domains in hybrid cloud environments
Home Office Phishing Scam Targets UK Immigration Sponsors
The sophisticated campaign aims to steal credentials of sponsor license holders to facilitate immigration fraud, extortion and other monetization schemes
Cybercriminals Exploit Low-Cost Initial Access Broker Market
Rapid7 found that threat actors are able to purchase low-cost initial access broker services, with many packages offering a variety of options
MITRE: Russian APT28's LameHug, a Pilot for Future AI Cyber-Attacks
While “fairly primitive”, APT28’s LameHug was a testbed for future AI-powered attacks, said two MITRE experts during Black Hat USA 2025
Financial Services Could Be Next in Line for ShinyHunters
New threat intelligence points to targeting of financial services and technology sectors by ShinyHunters group
Hackers Raid Dutch Lab, Stealing Data on 500,000 Patients
Threat actors have stolen data on at least half a million cancer screening patients